
i don't hunt bugs anymore. this is the setup that does it for me
文章目录
ai does the hunting now. i pick the targets, sort out the mfa and captchas it can't get past, read every report before it goes in, hit submit and reply to the platforms. everything in between runs on its own
this is the whole setup in one place. what it runs on, how the traffic moves, what it costs and what still needs me. no programs, no targets, nothing u can't already grab from my repos
if u want the which model and how to start side first, that's in my DMs article https://x.com/mdp_sec/status/2115614748742218045
how it got here
i started building it in feb and it kept changing the whole way. i only started tracking every run properly in aug, so the run numbers below start there
what runs now is a multi-agent pipeline split into phases. recon, access, a wide sweep across bug classes, triage, escalation, validation, a dupe check, then a report package lands with me
where it runs
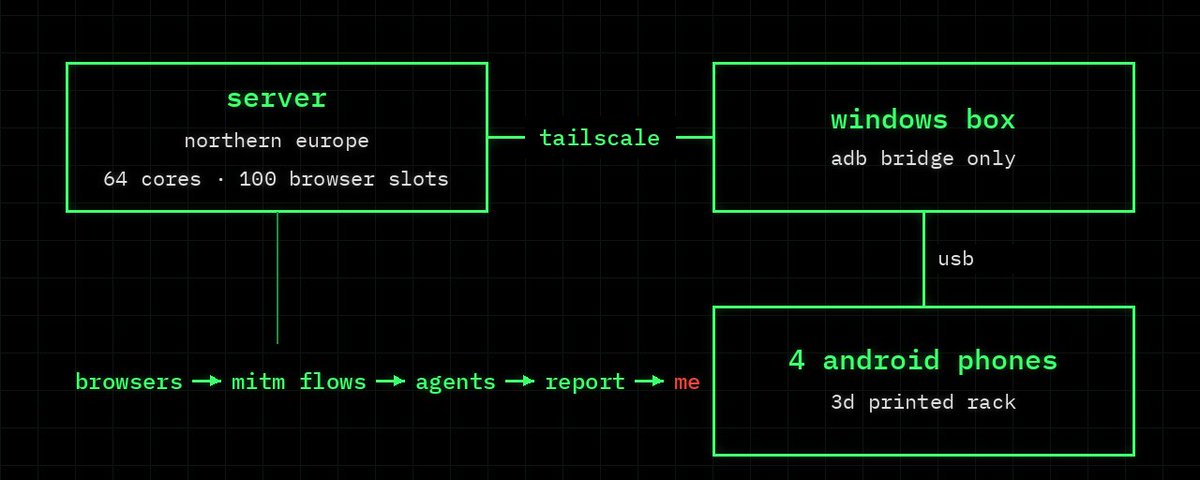
one Hetzner box in northern europe. 64 cores, 128 GB ram, 1.8 TB nvme, linux. about €300 a month. every agent and every browser lives on it
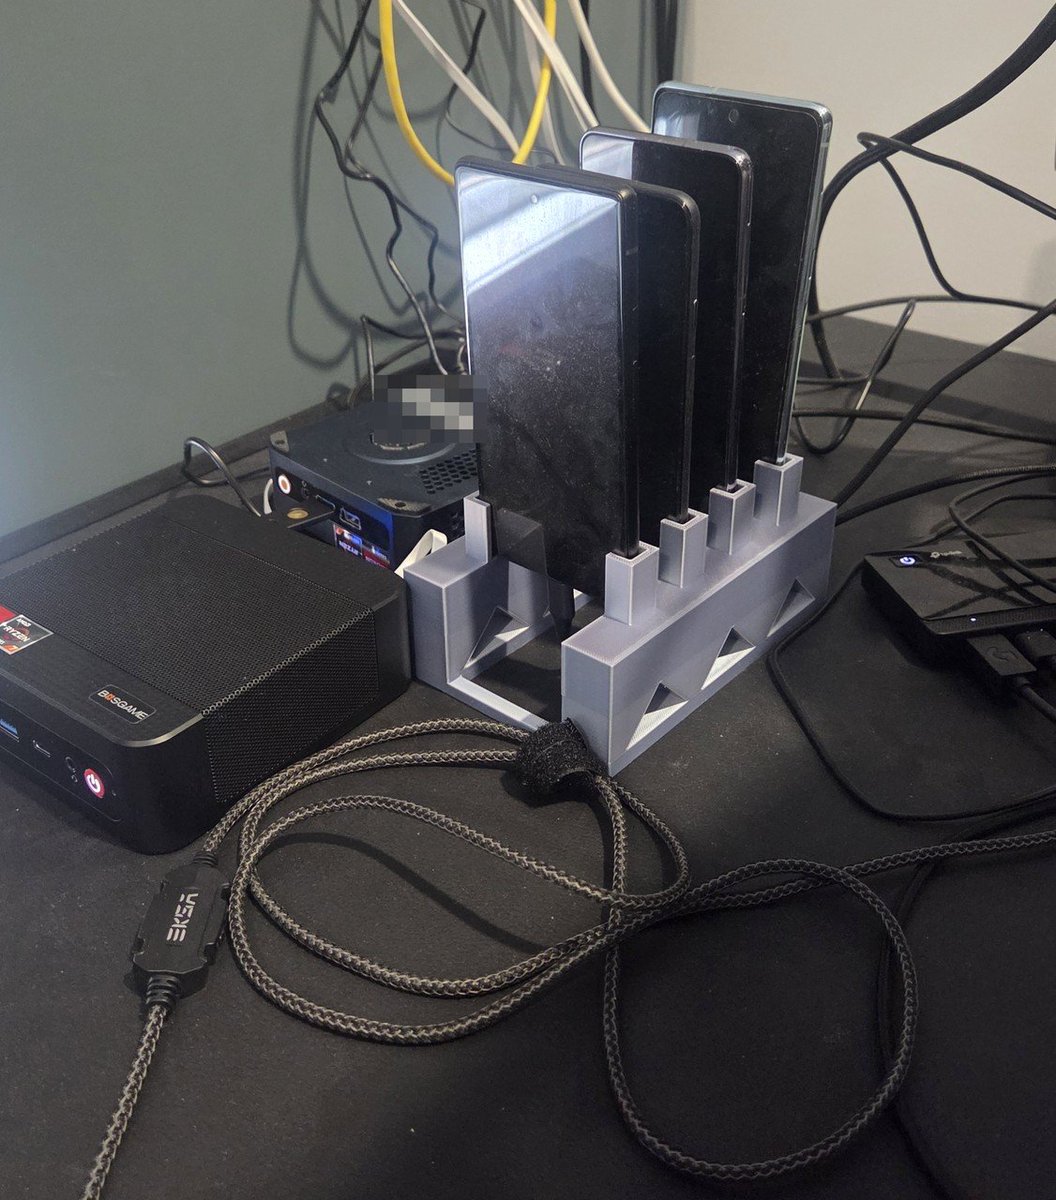
four android phones. pixel 5, pixel 6a, s20 fe and s21. some rooted, some not, because i need both for proper mobile testing. they sit in a 3d printed rack, plugged into a windows box over usb. that windows box is only there as the adb bridge so the server can drive the phones. it does no hunting
everything talks over tailscale. server, windows box, phones. no port forwards, and it acts like one local lab even though the server is in another country
100 browser slots, one mitm flow each
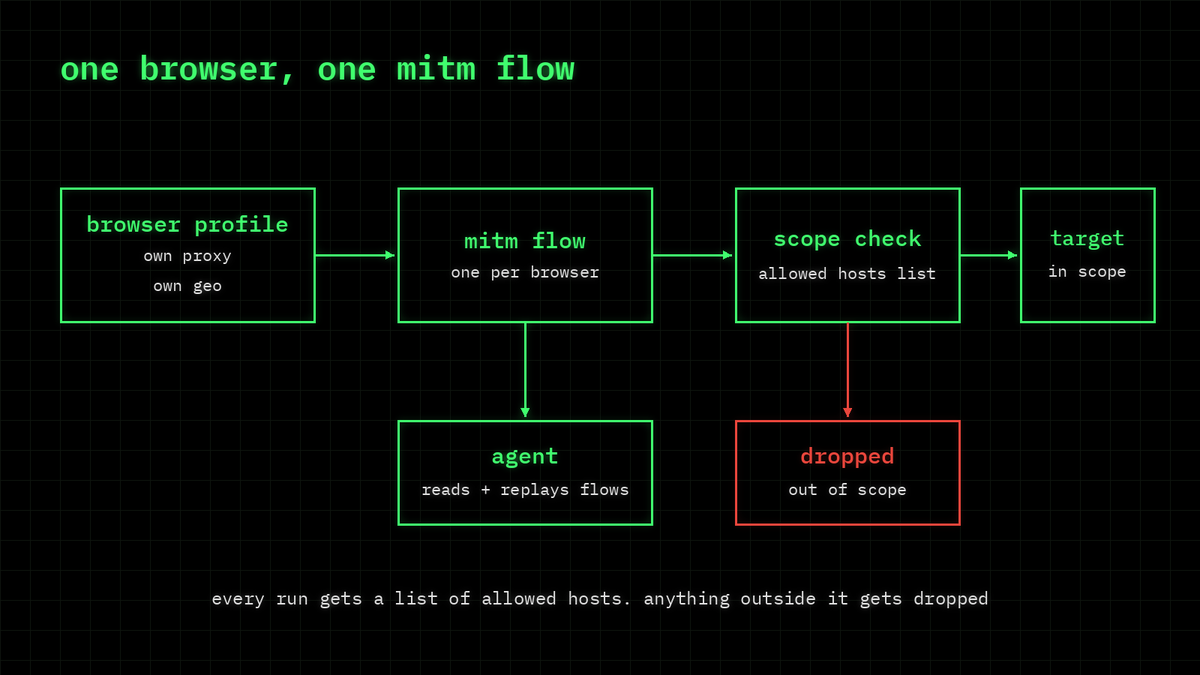
the server runs 100 browser slots. headed camoufox inside a virtual display, with chrome as the fallback when a site won't play nice. each profile keeps its own proxy and its own geo
traffic goes through mitmproxy, one flow per browser. login usually happens on normal browser tls first, then once the session is stable it can switch over to mitm for capture
every run gets a list of allowed hosts. anything outside it gets dropped. anything that changes state only ever touches my own test accounts or fresh objects it made itself. two accounts per target, A and B, so an access control check always has a victim that's mine
never liked mcp for this, way too much token usage. the agent just reads and replays the flows. haven't opened burp in ages
what one run looks like
-
load the scope for the target i picked
-
map the web, api and mobile surface
-
set up the two test accounts
-
map the endpoints and operations
-
sweep the bug classes
-
kill weak leads with controls
-
go deeper on the ones that hold up
-
check impact, severity, scope and that it reproduces
-
check for dupes against what's already known
-
write the report package
a run averages about 14 hours, median about 9. a few model families split the work. cheaper ones go wide, stronger ones do escalation and validation, and a different provider gives an independent second look
where it's been strongest: auth and access control bypass, idor and tenant boundaries, info disclosure, leaked keys, ssrf and some api and mobile stuff. complex business logic chains and fussy browser-only behaviour are still weak
where i come in
i choose the programs and targets. ai doesn't touch anything outside the scope i hand it
when it hits mfa, a captcha, kyc or anything it can't safely get past, it stops and hands it to me. across 1,024 runs that averaged about 0.59 hand-offs a run
nothing goes in just because a model said it's ready. i reread the report, the evidence and where the program is at, then i submit. platform replies, disputes and retests are mine too. i retest every 14 days while something's open so nobody gets to say not reproducible
why the runs dropped
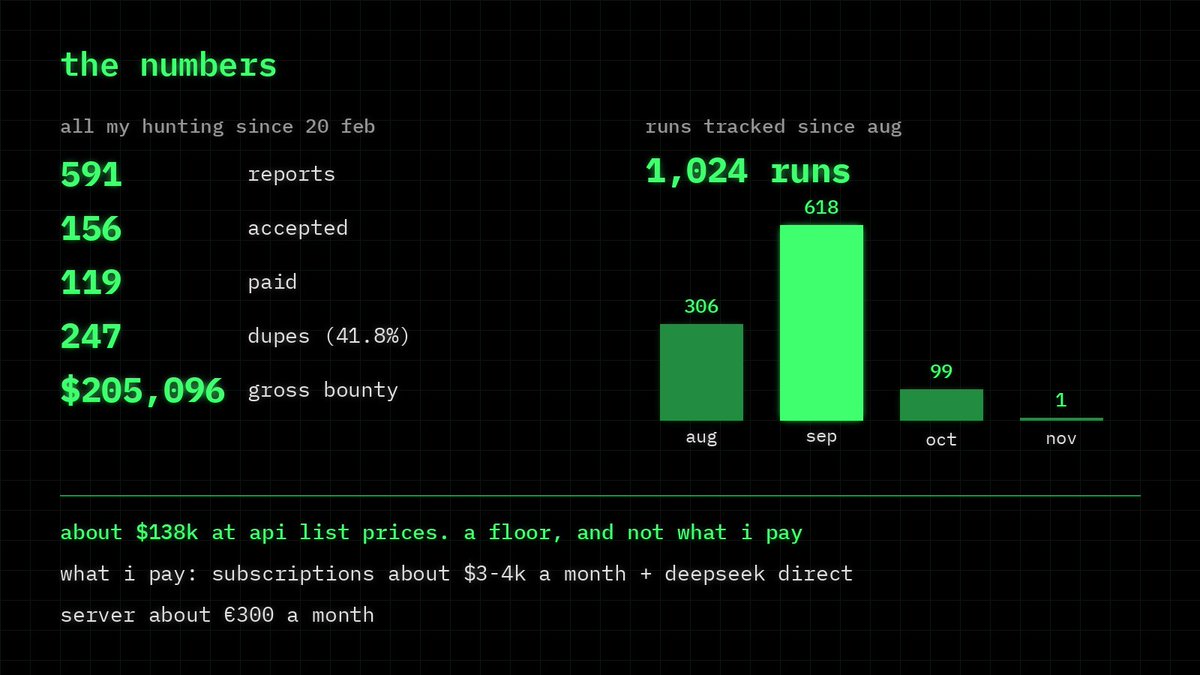
618 runs in sep. 99 in oct. 1 so far in nov
i got it fully automated and lost interest in hunting. for me it was always about the building and automating, more than finding more or getting paid more. once it was built i moved on to building BB Arena and other rabbit holes. my rabbit holes run about 6 to 8 months, then i get bored and go find the next one. feb to the slowdown lines up with that
two things wore me down. dupes, so much work done for free. and triage follow-ups. like 95% of the work is post submit
the numbers
all my hunting since the first report on 20 feb 591 reports 156 accepted, 119 of those paid 247 dupes (41.8%) $205,096 gross bounty
runs tracked since aug 1,024 runs 306 aug, 618 sep, 99 oct, 1 nov
what it costs
this is the bit people get wrong
the logs say those 1,024 runs burnt about 397.7 billion tokens. at api list prices that's about $138k. more than half those tokens have no price in the logs, so that's a floor
i don't pay that. most of it runs on subscriptions, grok, openai and claude, about $3-4k a month all up. deepseek is about 80-90% of my usage and i pay that direct, whatever the token burn is. the server is about €300 a month on top
hunting has a bunch of other costs and apis too, but its nothing compared to the subscription costs for tokens
what u can grab
the prompts are open. pretty much every prompt in my system is in there, minus the helpers https://github.com/mdpsec/bug-bounty-hunting-prompts
should i submit is the other one. i built it because people kept submitting reports that should never have gone in. it checks one finished report against the program rules before u hit submit https://github.com/mdpsec/should-i-submit
a small version of all this is one linux box, one isolated browser profile, one phone if u care about mobile, a scope file, two test accounts u own, and u reading every report before it goes anywhere
whats the one part of ur setup u still do urself


